


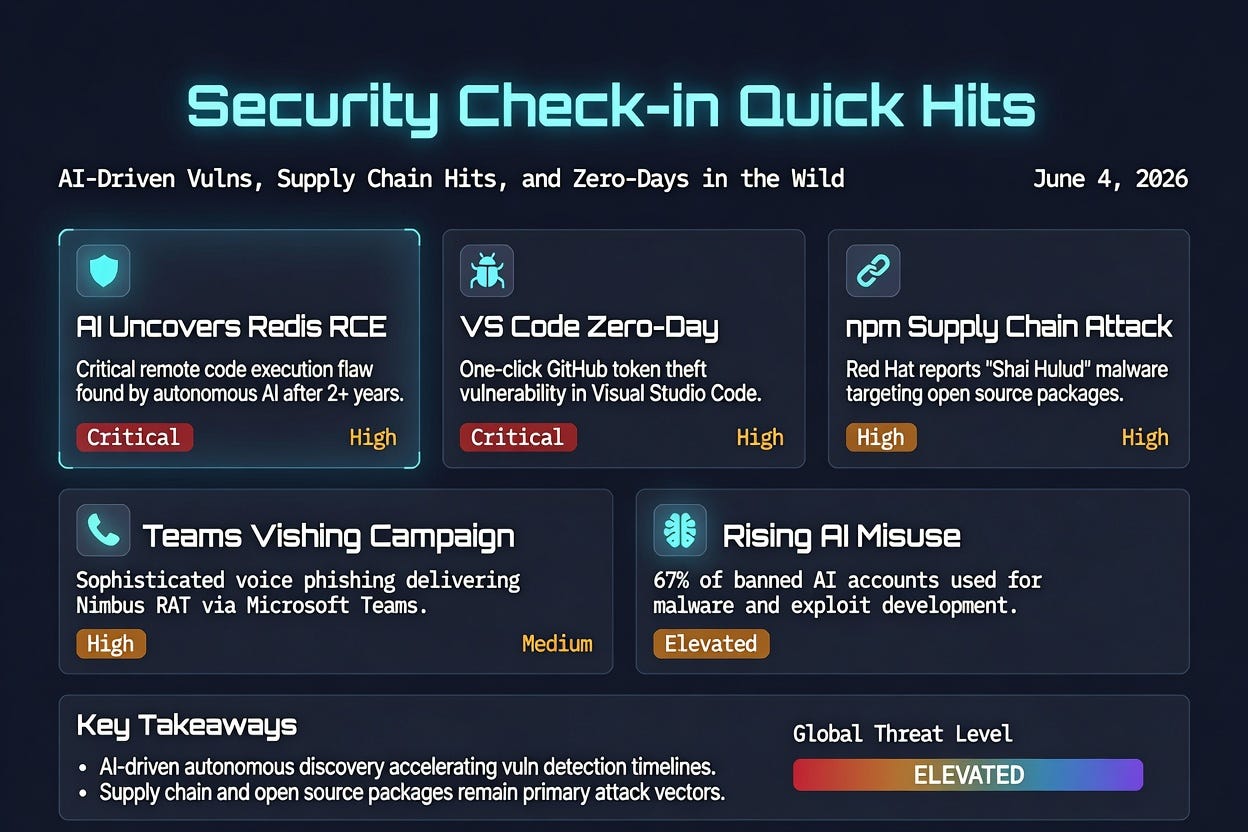
AI Autonomously Discovers Long-Standing Redis RCE Vulnerability
An autonomous AI tool recently uncovered a critical remote code execution (RCE) flaw in Redis (CVE-2026-23479) that had gone unnoticed for over two years. The vulnerability, introduced in Redis 7.2.0, allows authenticated users to execute OS commands on the server and affected multiple stable branches until patches rolled out on May 5.
Why it matters: This highlights the accelerating role of AI in both defense and offense. As AI tools scan codebases faster than human teams, organizations must prioritize rapid patching cycles. Redis users should ensure they’re on the latest patched versions and review authentication controls tightly.
Takeaway: AI is now finding what humans missed—your security tooling needs to keep pace.
VS Code Zero-Day Enables One-Click GitHub Token Theft
A zero-day vulnerability in Visual Studio Code allows attackers to steal GitHub tokens with a single click, posing a severe risk to developers and organizations relying on VS Code for workflows.
Details: The flaw exploits how VS Code handles certain URIs or extensions, potentially leading to credential compromise and subsequent supply chain attacks via compromised repositories.
Mitigation steps:
Update VS Code immediately.
Use token scopes minimally.
Monitor GitHub for suspicious activity.
Consider disabling certain protocol handlers if not needed.
This reinforces the need for vigilance in development environments, where tools trusted daily can become attack vectors.
Red Hat Discloses Sophisticated npm Supply Chain Attack
Red Hat revealed details of a supply chain attack involving malicious npm packages, dubbed “Shai Hulud” malware, which exploited GitHub in a targeted breach.
Impact: Attackers compromised open-source ecosystems by injecting backdoors into popular JavaScript packages, affecting downstream users who pulled in the tainted dependencies.
Lessons learned:
Verify package sources and use tools like npm audit.
Implement dependency scanning in CI/CD pipelines.
Adopt SBOM (Software Bill of Materials) practices for visibility.
Supply chain attacks continue to rise as attackers target the trust placed in open-source repositories.
Microsoft Teams Vishing Campaign Deploys Nimbus RAT
Cybercriminals are using sophisticated vishing (voice phishing) attacks via Microsoft Teams, combining email flooding and Quick Assist to deploy the Nimbus Remote Access Trojan (RAT).
How it works: Attackers flood targets with notifications, then guide them through “support” steps that install malware, giving full remote control.
Defense recommendations:
Train employees never to accept unsolicited Teams calls for tech support.
Enable MFA and review device enrollment policies.
Monitor for unusual Quick Assist usage.
Social engineering remains highly effective, especially when leveraging trusted collaboration platforms.
Rising AI Misuse in Cyberattack Preparation
Security reports indicate that approximately 67% of banned accounts on a major AI platform were using the models to prepare cyberattacks, including malware development and vulnerability identification.
Broader trend: Attackers are shifting from manual efforts to AI-automated workflows, accelerating exploit development and scaling operations. Combined with reports of cloud service abuse (AWS, Azure, Google Cloud) to mask malicious activity, the threat landscape is evolving rapidly.
Action items:
Monitor for anomalous AI usage in your environment.
Strengthen detection for AI-generated code and scripts.
Invest in AI-powered defensive tools that match the offense.
Final Thoughts
Today’s quick hits show a clear pattern: AI is supercharging both discovery of vulnerabilities and the attacks themselves, while supply chain and social engineering vectors persist as high-impact risks. Organizations should focus on timely patching (especially CISA KEV-listed items like PAN-OS flaws), rigorous supply chain hygiene, and user awareness training.
Stay vigilant—the speed of threats is increasing, and proactive defense is non-negotiable. Check back tomorrow for the next Security Check-in.